



Binance’s $6.3 Billion Hack: How a Compromised Engineer’s Laptop Triggered the Biggest Crypto Heist in History
October 30, 2026 | By JL HOUSSEM | Security & Cryptocurrency
Binance suffered a security breach involving approximately $6.3 billion in digital assets, potentially making it the largest cryptocurrency theft ever recorded. Investigators suspect North Korea-linked hackers, while blockchain companies and crypto issuers have already frozen billions. But the incident raises a more troubling question: how could a compromised employee’s laptop give attackers access to billions of dollars?
The Biggest Crypto Heist Yet: What Happened at Binance?
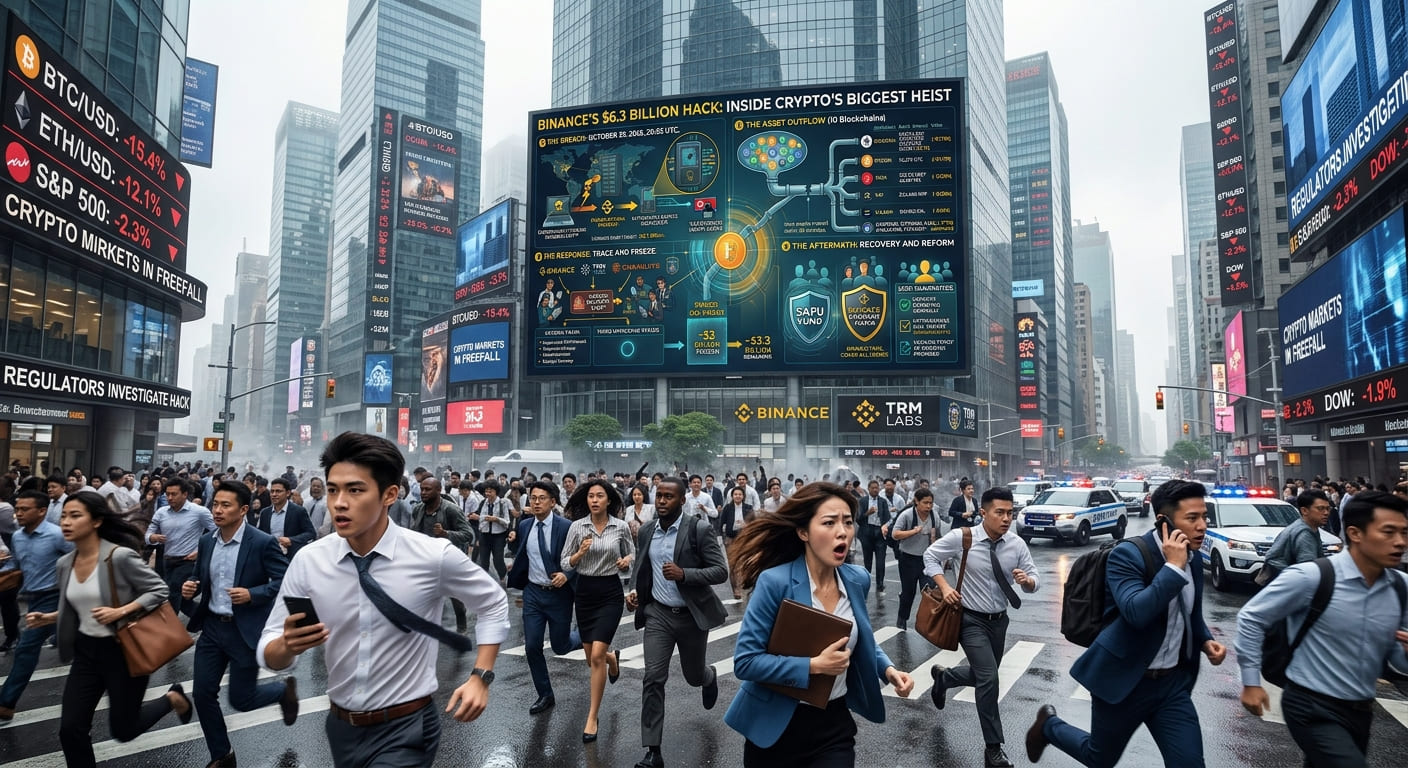
The cryptocurrency industry faced one of its most serious security crises on October 29, 2026, after attackers moved approximately $6.3 billion in digital assets out of wallets associated with Binance, the world’s largest cryptocurrency exchange.
The scale was extraordinary. According to blockchain intelligence firm TRM Labs, approximately $6.36 billion was transferred across ten blockchain networks, with most of the activity occurring within roughly 20 minutes.
The incident quickly became a race between the attackers and an international network of blockchain investigators, cryptocurrency companies, and asset issuers attempting to identify and freeze the stolen funds.
By October 30, Binance reported that approximately $3 billion in affected assets had been frozen through cooperation with blockchain partners.
That figure, however, requires an important distinction: frozen assets are not necessarily recovered assets. Freezing can prevent an attacker from transferring or converting certain tokens, but it does not automatically return ownership to their rightful holders.
The remaining funds became the central concern for investigators, particularly as analysts monitored transactions across multiple blockchain networks.
According to Binance’s preliminary investigation, the breach may have originated from a compromised laptop belonging to one of its DevOps engineers.
The company said the attacker used access to an internal service container to submit unauthorized withdrawal transactions. Binance also stated that it had found no evidence that cryptocurrency wallet private keys had been leaked.
This distinction matters. The incident may not have involved the traditional theft of private keys. Instead, it appears to have exploited the systems responsible for authorizing transactions.
How Could One Compromised Laptop Put $6.3 Billion at Risk?
The most concerning aspect of the Binance incident is not simply the amount of cryptocurrency involved. It is the apparent route through which the attackers gained access.
DevOps engineers work on the infrastructure that connects software development, deployment, monitoring, and operational systems. Their access can be powerful because they help maintain the services that keep large technology platforms running.
According to Binance, the compromised laptop allowed an attacker to reach a service container and initiate unauthorized withdrawals.
In simple terms, the attacker may not have needed to steal the keys to Binance’s wallets directly. Instead, the objective appears to have been to compromise the system that could request or authorize transactions.
This is a different category of security failure.
A cryptocurrency wallet can remain technically protected while the infrastructure controlling its transactions becomes vulnerable.
TRM Labs has provided additional technical details about the attack. Its analysis indicates that the attackers used an Ethereum mechanism known as EIP-7702, which allows an externally owned account to temporarily execute smart-contract code through an authorization mechanism.
The firm’s findings suggest that the attackers prepared authorizations in advance and used them to make a Binance hot wallet execute malicious transactions.
For non-technical readers, the important point is that the attackers may have manipulated the transaction authorization process rather than simply extracting a wallet’s secret key.
This creates a difficult security challenge for exchanges: protecting private keys is essential, but it is not enough if the software and personnel responsible for using those keys can be compromised.TRM Labs+2
Where Did the $6.3 Billion Go? The Race to Freeze Stolen Crypto
Unlike traditional bank transfers, cryptocurrency transactions are recorded on public blockchain networks. This creates an unusual situation for investigators.
They can often follow stolen assets from one address to another, identify suspicious transaction patterns, and monitor attempts to exchange or move funds.
However, visibility does not necessarily mean control.
Once cryptocurrency moves through decentralized exchanges, lending protocols, multiple blockchain networks, and other services, tracing the funds can become increasingly complicated.
The Binance incident demonstrated both sides of this system.
According to TRM Labs and other blockchain investigators, the stolen assets moved across multiple networks, including Ethereum, Bitcoin, Tron, Solana, and others.
Meanwhile, major cryptocurrency companies helped restrict the movement of some assets.
Among the companies involved were:
- Tether: The issuer of USDT, which can freeze tokens associated with identified blockchain addresses.
- Circle: The issuer of USDC, which also has the technical ability to block certain transfers.
- Arbitrum: Its Security Council reportedly intervened to restrict assets connected to the attack.
- Blockchain intelligence firms: Companies such as TRM Labs and Chainalysis helped identify suspicious transactions and coordinate with industry partners.
Independent blockchain analysis by Bitquery also tracked the movement of funds and reported that substantial amounts remained under attacker-controlled addresses after some assets had been frozen.
The most important lesson is that cryptocurrency investigations increasingly depend on cooperation between exchanges, token issuers, blockchain networks, and law enforcement agencies.
The blockchain may be decentralized, but the recovery process often depends on centralized companies that can intervene in specific circumstances.Bitquery+3
Is North Korea Behind the Binance Attack?
Several blockchain intelligence companies have attributed the attack to North Korea-linked hackers, although the investigation remains ongoing.
TRM Labs identified the suspected attackers as TraderTraitor, a hacking group associated with North Korea.
Chainalysis also expressed high confidence in North Korean involvement, according to CNN’s reporting.
These assessments are based on similarities between the Binance incident and previous attacks, as well as intelligence gathered from blockchain transactions and information outside the blockchain.
The suspected involvement of North Korea is significant because cryptocurrency theft has become an important source of illicit revenue attributed to groups linked to the country.
According to US authorities and international investigators, North Korean hacking operations have targeted cryptocurrency exchanges, financial institutions, and blockchain projects over several years.
One of the most notable examples was the February 2025 attack on Bybit, in which approximately $1.5 billion in cryptocurrency was stolen.
The FBI attributed that incident to North Korean actors.
If the Binance attribution is confirmed, it would represent another enormous escalation in the scale of cryptocurrency theft associated with these groups.
However, attribution should not be confused with a final legal determination. North Korea has previously denied allegations of involvement in cyberattacks, and the Binance investigation has not yet produced a publicly established judicial conclusion.TRM Labs+2
Binance Promises to Cover All Losses: Are User Funds Safe?
Binance moved quickly to reassure customers.
In its October 30 announcement, the company said it would cover all losses using its corporate funds and its Secure Asset Fund for Users, commonly known as SAFU.
The exchange also stated that user funds remained safe.
As an immediate response, Binance:
- Temporarily suspended deposits and withdrawals while conducting security checks.
- Revoked authorization associated with the affected address.
- Contacted law enforcement agencies.
- Worked with blockchain intelligence partners to trace and freeze assets.
- Promised to publish a detailed technical post-mortem after completing its investigation.
- Announced plans to update its Proof of Reserves after remediation.
These measures are important, but customers should distinguish between a company’s financial promise and independently verified evidence of its financial position.
Binance’s commitment to cover losses is a significant assurance. Nevertheless, the market will need more than statements to assess the long-term consequences.
An updated Proof of Reserves, a detailed technical investigation, and transparent information about the remaining affected assets will be particularly important.
There is also a wider question about the role of SAFU.
The fund was designed to provide an additional layer of protection for Binance users. However, a breach estimated at $6.3 billion is far beyond the scale of many previous exchange incidents.
It places the company’s financial resources and ability to maintain confidence under considerable scrutiny.Binance Support+2
Binance Is Not the First: How the Attack Compares With Bybit
The cryptocurrency industry has experienced several major thefts, but the reported scale of the Binance incident puts it in a different category.
The previous record was widely associated with the February 2025 Bybit hack, which involved approximately $1.5 billion.
The Binance incident’s estimated $6.3 billion impact is more than four times that amount.
This comparison also reveals how quickly the financial scale of cryptocurrency attacks has expanded.
| Incident | Approximate amount |
|---|---|
| Binance – October 2026 | $6.3 billion |
| Bybit – February 2025 | $1.5 billion |
The comparison is based on reported amounts and does not imply that every incident involved the same attack method or recovery outcome.
What makes the Binance incident particularly important is the apparent exploitation of internal infrastructure rather than a straightforward attack on an individual user’s wallet.
It suggests that even the largest exchanges must consider employee devices, privileged access, transaction approval systems, and internal software services as potential attack surfaces.Investing.com+1
Why This Attack Could Change Cryptocurrency Security
The Binance incident exposes a structural weakness in the cryptocurrency industry: centralized exchanges remain attractive targets because they hold enormous quantities of digital assets on behalf of millions of customers.
Unlike traditional stock exchanges, cryptocurrency platforms often operate custody systems that control the actual digital assets users deposit.
This creates several potential vulnerabilities.
1. Employee devices are part of the security perimeter.
A compromised employee laptop can become an entry point into systems that have access to sensitive infrastructure. Exchanges therefore need stronger device isolation, privileged-access management, and continuous monitoring.
2. Transaction authorization needs independent protection.
Even if private keys are never stolen, attackers may exploit systems that authorize transactions. Multiple independent approvals, withdrawal limits, and automated anomaly detection can reduce this risk.
3. Hot wallets remain an important attack surface.
Hot wallets are connected to online systems, making them convenient for withdrawals and everyday operations. However, their connectivity also exposes them to cyberattacks.
Large exchanges need to carefully balance liquidity requirements with cold storage, transaction restrictions, and additional security controls.
4. Blockchain transparency has limitations.
Public transaction records make tracking possible, but they do not guarantee recovery. The ability to freeze certain stablecoins also depends on the issuer’s intervention powers, which do not apply equally to every cryptocurrency.
In other words, blockchain transparency can help investigators understand where money goes, but it cannot independently force an attacker to return it.
Cryptocurrency Markets React to the Binance Security Crisis
The breach also affected cryptocurrency markets.
Bitcoin and Ether experienced sharp declines following reports of the incident, reflecting concerns about the security of centralized exchanges and the potential consequences for investor confidence.
According to the figures reported by CNN, both assets had recovered part of their initial losses by Friday, October 30, but remained approximately 2% to 3% lower around midday in Hong Kong.
Reuters also reported declines in shares of cryptocurrency-related companies during the market reaction.
However, it would be premature to interpret these movements as evidence of a broader collapse in cryptocurrency demand.
The incident primarily raises questions about exchange security, custody arrangements, and operational risk.
Investors may continue to support Bitcoin and Ethereum while simultaneously becoming more cautious about where they store their assets.
That distinction is important: a security failure at an exchange does not automatically mean the underlying blockchain networks have been compromised.Investing.com+2
The Bigger Question: Can Any Crypto Exchange Be Completely Secure?
For years, cryptocurrency exchanges have promoted security infrastructure, proof-of-reserves mechanisms, insurance arrangements, and institutional-grade custody solutions as ways to build trust.
But the Binance incident highlights an uncomfortable reality: security is not determined by wallet technology alone.
It also depends on employees, internal software, authorization processes, third-party services, and the ability to detect unusual activity before damage becomes irreversible.
There is an important distinction between proving that an exchange holds sufficient assets and proving that its operational systems cannot be manipulated.
Proof of Reserves can provide useful information about an exchange’s reported assets and liabilities, depending on its methodology. It is not, by itself, a cybersecurity audit or a guarantee against unauthorized withdrawals.
This is where the industry needs to improve.
Exchanges should increasingly be judged not only by trading volume and liquidity but also by the transparency of their security architecture, the independence of their audits, and their ability to demonstrate how they respond to major incidents.
Our Take: The Real Weakness Was Not Necessarily the Wallet
The most interesting aspect of the Binance incident is the possibility that the attackers did not need to defeat the cryptographic protection of the wallets themselves.
Instead, they may have compromised the infrastructure responsible for authorizing transactions.
If that explanation is confirmed by Binance’s final technical investigation, the implications extend well beyond one exchange.
It would demonstrate that protecting private keys is only one part of cryptocurrency security. The systems surrounding those keys can become equally valuable targets.
There is also a troubling economic dimension.
When attackers can move billions of dollars across several blockchain networks in minutes, the traditional idea of responding to a cyberattack after discovering it may no longer be sufficient.
Security systems need to identify abnormal behavior and prevent unauthorized transactions before they are completed.
For Binance, the immediate challenge is to demonstrate that customer funds remain protected and that the vulnerabilities behind the incident have been addressed.
For the wider cryptocurrency industry, the challenge is much larger: rebuilding confidence in a financial infrastructure where a single compromised access point could potentially expose billions of dollars.
The biggest question is no longer simply how much cryptocurrency was stolen. It is whether the industry can prevent the next attack before billions leave the system.
External Sources & Further Reading
1. Reuters: Binance $6.3 Billion Crypto Heist
2. TRM Labs: North Korea Steals $6.36 Billion From Binance
3. Associated Press: North Korea Linked to Binance Crypto Hack
4. CoinDesk: Binance $6 Billion Security Breach
5. Cointelegraph: Binance Engineer’s Hacked Laptop and $6.3B Breach

Independent technology writer focused on artificial intelligence, emerging technologies, and digital innovation. Covers AI applications in sports, productivity, and online business.